
The AI Threat in the Scamiverse: Protecting Corporate Assets from High-Precision Deepfakes
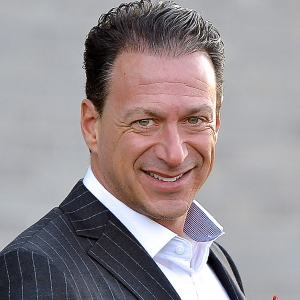
By Robert Siciliano, CSP, CSI, CITRMS
The traditional digital perimeter has collapsed. The current era is defined by the “Scamiverse”—a high-velocity environment dominated by organized crime syndicates leveraging human-trafficked labor. The primary target of cyber-predators is no longer organizational software, but the “Wetware”: the human brain. The most severe risk to financial institutions, real estate transactions and personal legacies is the “Perfect Lie,” executed via AI-driven deepfakes and voice cloning.
Surviving this reality requires abandoning the “Compliance Trap” of passive training. Organizations must bridge the Security Appreciation Gap and engineer a Strategic Human Firewall™—a defense system built to neutralize the Human Blindspot™ before funds are ever compromised.
Phase I: The Evolution of the Scamiverse
Historically, threat detection relied on identifying poor grammar or clumsy formatting. That era is over. With hundreds of thousands of AI-powered attacks reported annually in the U.S., the technical barrier to entry for cyber-predators has evaporated. Threat actors now deploy Generative Adversarial Networks (GANs) and platforms like FraudGPT and GhostGPT to craft sophisticated, targeted campaigns.
Human identities can be cloned for as little as $5. In high-stakes industries like finance and real estate, these “Digital Puppets” are weaponized to facilitate catastrophic wire fraud by mimicking executives, attorneys and sellers with flawless precision.

Phase II: The Arsenal of Digital Deception
Modern spoofing relies on three primary vectors combined with advanced AI tactics to construct the “Digital Mask”:
- Voice Synthesis & Phone Spoofing: Criminals manipulate caller ID to display familiar local numbers while utilizing AI voice cloning. By analyzing vocal biomarkers—pitch, accent and breathing—from just 3 to 30 seconds of scraped audio, predators can impersonate trusted individuals. The ultimate red flag is a demand for immediate payment via wire transfer or cryptocurrency.
- Technical Exploits & Email Spoofing: Attackers exploit DomainKeys Identified Mail (DKIM) signatures and misconfigured DNS records, allowing malicious emails to bypass security filters while appearing to originate from legitimate domains. Once in an inbox, the perceived legitimacy is used to issue fraudulent legal notices or payment demands.
- Neural Puppetry & URL Spoofing: Phishing campaigns utilize deceptive hyperlinks or minor character swaps in domains. Simultaneously, GANs generate hyper-realistic fake video content. Sophisticated attackers can inject pre-generated or real-time AI video into platforms like Zoom, transforming the person on screen into a literal “Digital Frankenstein.”
Phase III: Exploiting the Human Blindspot™ — The Cognitive Fallacy
Current industry standards for security training rely heavily on the prefrontal cortex—the part of the brain responsible for logic, reasoning and complex planning. The fundamental assumption is this: If we give employees enough data—policies, compliance videos and simulated phishing results—they will rationally apply that data when an attack occurs.
These attacks succeed not from a lack of awareness, but due to biological programming. Humans instinctively “Default to Trust.” When presented with a familiar voice or face, critical thinking is bypassed in favor of an inherent “Action Bias.”
Criminals exploit this biological vulnerability through psychological mechanisms including:
- Manufactured Urgency: Fabricating crises—such as expiring deals, tax penalties or family emergencies—pushes targets toward a high-speed emotional reaction before they have time to verify the source.
- Technical Credibility: Accurate logos, convincing domain information and functional-looking portals can lower natural vigilance.
This biological hijacking results in Silent Failure: a catastrophic data or financial breach that may trigger no technical alarms because an authorized human initiated the action.
Phase IV: Constructing the Strategic Human Firewall™
Evolving an organization beyond Passive Security Theater by incorporating the active defense of a Strategic Human Firewall™ is a necessary, yet challenging, step. While adding this foundational human layer is tactically superior for actual defense, it demands more effort, creates intentional friction in business workflows by forcing pauses, and disrupts the comfort of relying solely on existing compliance metrics.
Combating AI requires transitioning from Security Theater—ineffective compliance exercises—to Security Appreciation, where protecting assets becomes a core, actionable value. This paradigm shift creates a Strategic Human Firewall™, turning a workforce from a potential liability into a proactive Human Sensor Network.
The cornerstone of this defense is the Triple-A Protocol, a strict “Break the Fake” playbook:
1. Analyze — Recognize Manufactured Urgency
When a request dictates secrecy or immediate action, a mandatory pause is required. The brain has entered an emotional state; taking a breath re-engages analytical thinking.
2. Authenticate — Identify the “Digital Mask”
Every digital communication must be treated as a potential breach. This involves inspecting technical headers, avoiding suspicious subdomains and remaining alert to the subtle biological and technical red flags of deepfakes.
3. Act — Execute Out-of-Band Verification
Contact information provided within a suspicious message must never be used. The required action is to disconnect and initiate a callback using a trusted, pre-validated number or a pre-established code word. Furthermore, strict credential hygiene and mandatory Multi-Factor Authentication (MFA) must be enforced across all critical portals. 
Because this methodology requires an intentional behavioral evolution—moving from passive compliance to active defense—it often triggers natural resistance from corporate leadership. Here are the top five objections currently defending legacy compliance programs, and the strategic rebuttals needed to shatter them.
By securing the Human Blindspot™ and mandating rigid verification reflexes, the extended perimeter against modern digital deception is successfully fortified.
Transform your workforce from a passive vulnerability into an active defense by bringing Robert Siciliano to your stage for an unforgettable, fully interactive keynote speech.
While routine phishing simulations only address a single, narrow vulnerability, Robert moves your audience beyond “check-the-box” compliance to build genuine Security Appreciation across every area of their personal and professional lives. Ignite true behavioral change, close the Human Blindspot™, and empower your team to build an unassailable Strategic Human Firewall™.
About the Author: Robert Siciliano
Robert Siciliano is a cybersecurity expert, #1 Amazon best-selling author and professional keynote speaker who has spent more than 30 years helping individuals and organizations better understand security, fraud prevention and the human behaviors that criminals exploit. Siciliano, CSP, CSI, CITRMS, is CEO of Safr.Me, Head Trainer at Protect Now LLC and the architect of the Strategic Human Firewall™. His work focuses on an increasingly important reality in cybersecurity: sophisticated technology alone cannot protect an organization when criminals can manipulate trusted employees into opening the door themselves.
That human dimension is at the heart of Siciliano’s approach to speaking and training. Rather than treating cybersecurity as a technical problem belonging exclusively to the IT department, he challenges employees and leaders to recognize their own role in protecting organizational assets. His interactive presentations explore AI-enabled fraud, deepfakes, voice cloning, social engineering, identity theft and the behavioral vulnerabilities behind today’s rapidly evolving scams. His current programs include “The Strategic Human Firewall™: Defending Against Deepfakes, AI, and Social Engineering.”
For audiences, the goal is not simply greater security awareness. Siciliano wants people to develop what he calls Security Appreciation—an understanding of cybersecurity that becomes personal enough to influence behavior when a convincing email, phone call, video or urgent request puts that knowledge to the test.
Book Cybersecurity Keynote Speaker Robert Siciliano
Organizations looking to prepare their people for AI-enabled scams, deepfakes, social engineering and the changing human side of cybersecurity can book Robert Siciliano through Speakers.com. Robert’s interactive keynote programs are designed to move audiences beyond “check-the-box” security awareness and toward practical behaviors that help employees recognize manipulation, verify suspicious requests and become an active part of an organization’s cybersecurity defense. Contact Speakers.com for Robert Siciliano’s current speaking fee, availability and program options.