
A series of widespread technology outages affecting major American banks, Microsoft Outlook, and the nation’s aviation system has exposed an unsettling vulnerability in our increasingly interconnected economy. When essential services depend on the same underlying technologies, a single technical failure can disrupt entire industries, leaving millions of customers and businesses unable to access systems they rely upon every day.
For cybersecurity expert and former FBI counterintelligence operative Eric O’Neill, the troubling question isn’t simply whether hackers are responsible. It’s whether America’s growing dependence on shared digital infrastructure has created systemic vulnerabilities that organizations are dangerously unprepared to confront. During a recent interview on NewsNation, O’Neill examined disruptions affecting Wells Fargo, JPMorgan Chase, Bank of America, and U.S. Bank, alongside separate outages involving Microsoft email services and the Federal Aviation Administration. Although the banks attributed their problems to technical issues rather than confirmed cyberattacks, O’Neill suggested that a shared technology provider or common infrastructure failure could explain why multiple institutions experienced similar difficulties.
The Danger of Putting Every Digital Egg in One Basket
O’Neill identified a fundamental weakness in the architecture of modern business technology: Organizations have increasingly consolidated essential operations around common cloud platforms, software providers, and interconnected systems. As he explained during the interview, “We put all our eggs in one basket. That basket is up in the cloud.” The advantages of this technological consolidation are considerable. Shared infrastructure can reduce costs, streamline operations, and allow organizations to deploy sophisticated digital services without maintaining extensive independent systems. But those efficiencies can introduce a dangerous concentration of risk. When a widely used technology fails, the consequences can cascade across businesses that otherwise have little in common. O’Neill pointed to the 2024 CrowdStrike software update failure, which disrupted airlines, hospitals, businesses, and other organizations worldwide, as a powerful example of how a technical malfunction can produce consequences resembling those of a major cyberattack. His concern extends beyond temporary inconvenience. When customers repeatedly lose access to banking services, communications platforms, or transportation networks, the damage can reach something far more difficult to restore than a computer system: public trust.
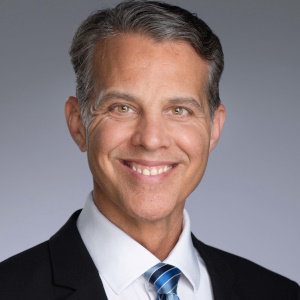
 Eric O’Neill discusses widespread technology outages on NewsNation
Why Cybersecurity Is No Longer Just About Stopping Hackers
O’Neill emphasized that financial institutions invest heavily in cybersecurity defenses, redundancy, and exercises designed to prepare for external attacks. Yet some of the most disruptive threats may emerge from ordinary technological failures that organizations have not adequately anticipated. The distinction matters. A software defect, infrastructure malfunction, or failed update can interrupt business operations just as effectively as malicious activity. And when numerous organizations depend on the same provider, even carefully designed internal safeguards may prove insufficient.
For corporate executives, the implications are significant. Cybersecurity and operational resilience can no longer be viewed exclusively as technical responsibilities delegated to IT departments. They are fundamental questions of organizational strategy, risk management, and business continuity. Leaders must understand not only how their own systems are protected, but also how dependent their operations have become on third-party technologies. That requires evaluating shared vulnerabilities, strengthening contingency plans, and ensuring that critical services can continue when essential digital infrastructure becomes unavailable.
O’Neill’s NewsNation interview underscores an increasingly important lesson for business leaders: The greatest threat to an organization’s digital operations may not always be a sophisticated hacker. Sometimes, it is the technology everyone has come to depend upon.
Book Cybersecurity Expert Eric O’Neill for Your Next Conference
A former FBI counterintelligence operative who played a pivotal role in exposing notorious spy Robert Hanssen, Eric O’Neill brings firsthand national security experience and cybersecurity expertise to corporate and association audiences. The author of Spies, Lies, and Cybercrime: Cybersecurity Tactics to Outsmart Hackers and Disarm Scammers, O’Neill delivers compelling keynote presentations exploring cybersecurity, artificial intelligence, espionage, digital threats, and the evolving challenges of protecting organizations in an interconnected world.
To inquire about Eric O’Neill’s availability for your next corporate conference, leadership meeting, or cybersecurity event, contact Speakers.com.